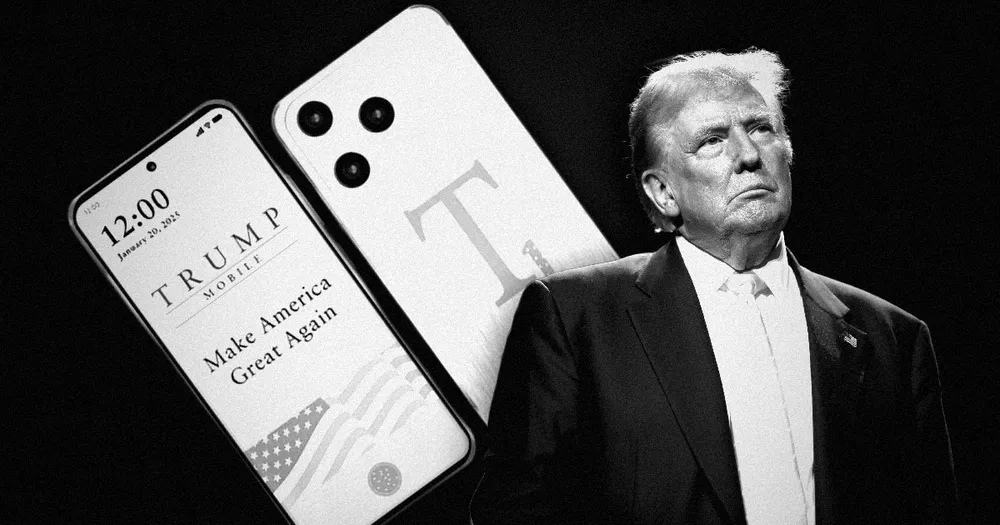
Hackers have released the personal details of thousands of Trump Mobile customers, the phone company launched by the Trump family last year.
A newly formed ransomware group calling itself BYOD published 3,615 customer records on 5 October. They include names, email addresses, phone numbers, home addresses and order details, according to Straight Arrow News and IBTimes.
The group says it got in by infecting an employee at Liberty Mobile, the Florida company that runs Trump Mobile's network service, with malware, then moved into Trump Mobile's own systems. It told International Cyber Digest that neither company used multi-factor authentication and that it is still inside. Those claims come from the hackers and have not been independently confirmed.
According to BYOD, when it told Trump Mobile about the breach, the company replied: "We have no team to handle this." Trump Mobile has not commented publicly.
It is not the company's first leak. In May, researchers found customers' email and home addresses exposed online, in a database that pointed to around 30,000 customers. Many customers have also waited months for the T1 phone they paid for.
If you are a Trump Mobile customer, assume your name, number and home address are public. Watch for phishing texts and calls that use your order details, and ask your carrier for a port-out PIN so your number cannot be moved without you.